Persistant Ways of PlugX RAT
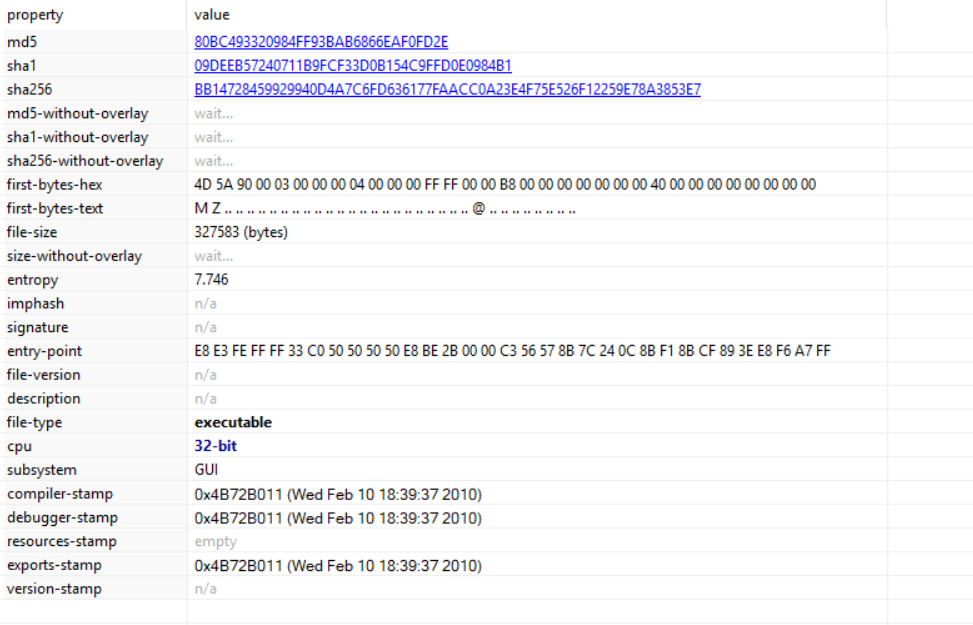
PlugX a Remote Access Trojan (RAT) was first identified in 2012. PlugX is known to be used against high profile government institutions and other organizations and has evolved since then. PlugX has also been seen as Korplug, SOGU and DestroyRAT. The primary functionality of this malware is to: Provide persistence access for adversaries. Perform surveillance of the infected machines. Reach out to a command and control server. Hijack legitimate executable and inject malicious code. Since the identification of PlugX in 2012, it has mutated in complexity and exploitation techniques. PlugX is commonly seen to be used in advanced targeted attacks, with capabilities to impersonate authentic processes and perform extensive recon on infected machines. The malware sample analyzed in this blog, has been downloaded from the internet. Basic Static Analysis The malware sample analyzed in th...